
How to Pen-Test a Multi-Tenant SaaS Application
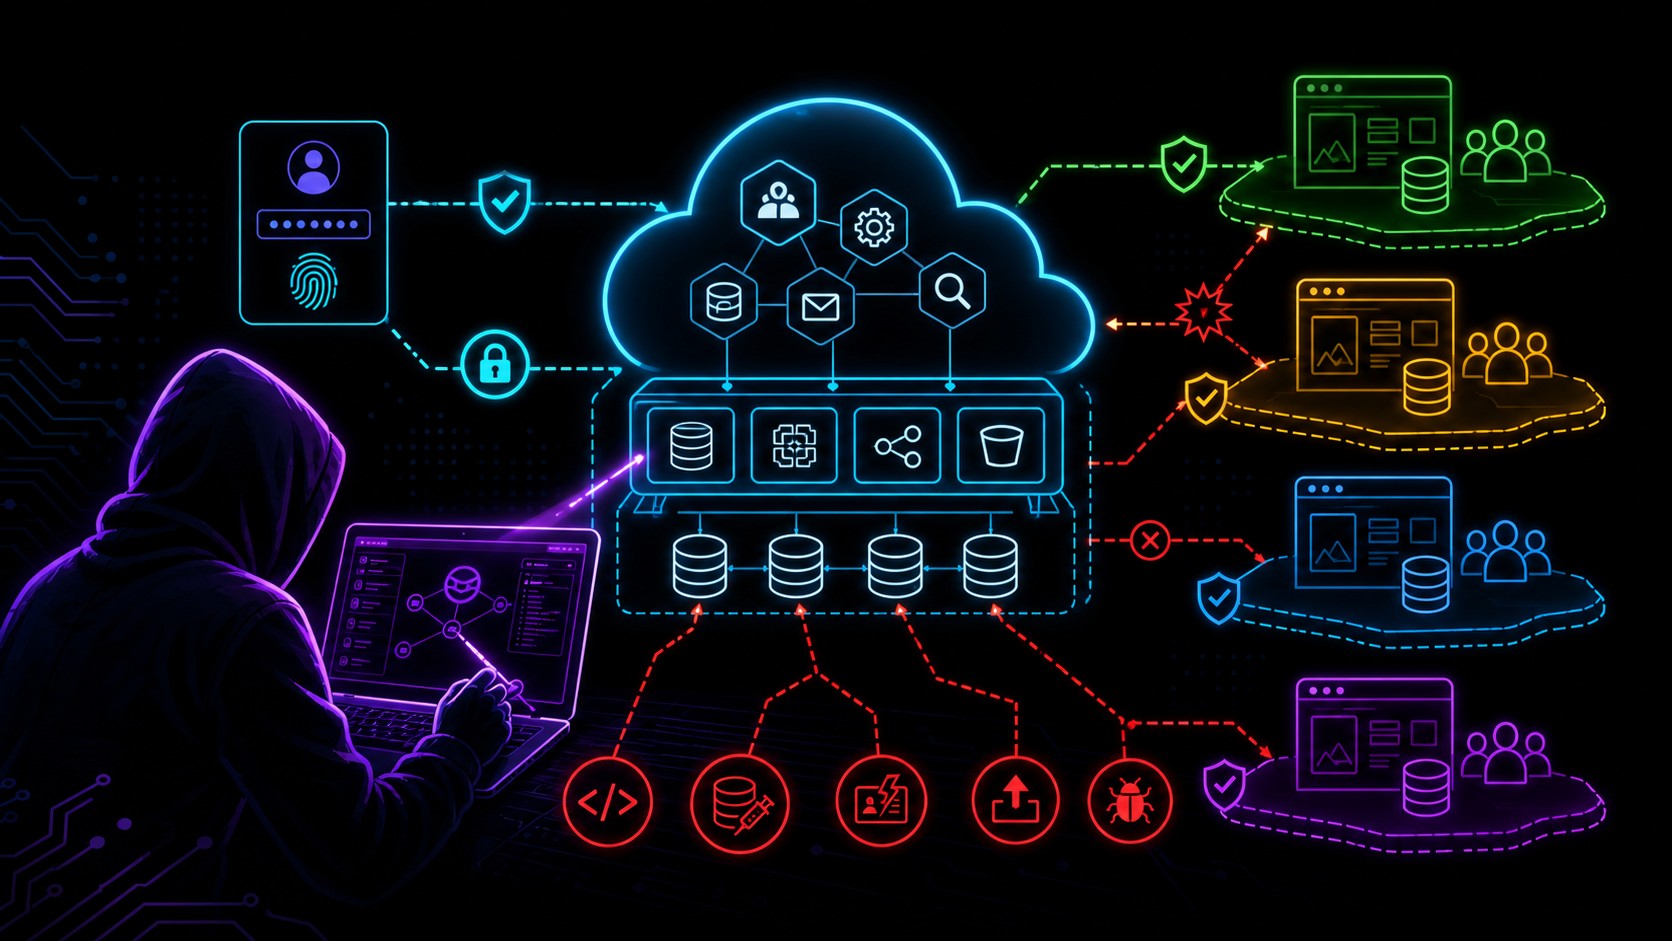
A multi-tenant SaaS application can pass a conventional penetration test and still expose one customer's data to another. Unlike single-tenant software, the greatest security risk is often not remote code execution or SQL injection, but broken tenant isolation. Effective penetration testing must therefore focus on proving that every authenticated user can access only the data, resources and workflows they are explicitly authorised to use.
The first objective of any SaaS penetration test should be validating tenant boundaries. Create multiple organisations populated with realistic data and verify that every API endpoint, search query, report and export remains scoped correctly. If changing an identifier, URL or request body allows data from another tenant to appear, the platform has a critical isolation failure regardless of how strong its authentication may be.
Authentication is only the starting point. After confirming users can log in securely, spend significantly more time testing authorisation. Attempt requests using administrator, standard user, read-only and external accounts. Verify that every protected endpoint independently checks permissions rather than relying on the client application. Hidden buttons and protected screens should never be mistaken for security controls.
Object-level authorisation deserves particular attention. Insecure Direct Object References (IDORs) remain one of the most common SaaS vulnerabilities because applications validate that a user is authenticated but fail to confirm they own the requested resource. Changing a case identifier, customer ID or document reference should never expose information belonging to another user or organisation.
Role testing should include unexpected scenarios rather than only valid configurations. Test accounts with missing roles, partially configured permissions, expired invitations and incomplete onboarding. Secure applications fail closed, denying access whenever sufficient authorisation information is unavailable. These edge cases frequently reveal assumptions that normal functional testing never exercises.
File handling is another common source of data leakage. Upload documents under one tenant, then attempt to download them using another. Verify that temporary URLs, previews, thumbnails and exported files all enforce the same access rules as the primary application. Storage services should never become an unintended bypass around the application's authorisation model.
API testing should extend beyond documented endpoints. Inspect network traffic, enumerate available routes and replay requests using tools such as Postman or curl. Where appropriate, modify identifiers, remove claims, alter headers and attempt operations in unexpected sequences. The goal is not to break the API through malformed input but to determine whether business rules are consistently enforced.
Modern SaaS platforms also benefit from strong observability during testing. Audit logs should record authentication events, failed authorisation attempts, administrative actions and cross-tenant access failures. These logs not only support investigations but also provide confidence that suspicious behaviour can be detected in production before it becomes a larger incident.
Automation is invaluable once manual testing has established the security model. Regression suites can repeatedly verify tenant isolation, permission boundaries and common privilege-escalation scenarios as new features are delivered. Embedding these tests into continuous integration helps prevent future changes from reintroducing vulnerabilities that were previously fixed.
Finally, remember that a penetration test should validate business rules, not just infrastructure. A secure login, encrypted traffic and patched servers are all important, but they mean little if one customer can accidentally access another customer's information. The strongest SaaS platforms are those that treat tenant isolation and authorisation as fundamental architectural principles, then continuously prove those assumptions through testing.
Successful penetration testing is ultimately about trust. Every customer expects their information to remain isolated, regardless of how many other organisations share the same platform. A thorough multi-tenant penetration test provides confidence that those boundaries remain intact, even as the application continues to evolve.

Share your thoughts